Free demo, latest questions, a year of free updates, instant delivery, and a refund policy with clear written terms — Prep4SureReview is built to serve every candidate's best interests on the PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) exam. All that remains is your commitment to the 418 practice questions for the ISO-IEC-27001-Lead-Auditor日本語 exam.
PECB ISO-IEC-27001-Lead-Auditor日本語 Exam Overview:
| Certification Vendor: | PECB |
|---|---|
| Exam Name: | PECB Certified ISO/IEC 27001 Lead Auditor |
| Exam Number: | ISO-IEC-27001-Lead-Auditor |
| Available Languages: | English, French, Portuguese, German, Spanish |
| Exam Format: | Essay-type questions, Multiple choice |
| Certificate Validity Period: | 3 years (with maintenance requirement) |
| Exam Duration: | 180 minutes |
| Related Certifications: | PECB ISO/IEC 27001 Foundation PECB ISO/IEC 27001 Lead Implementer |
| Exam Price: | USD 500 |
| Passing Score: | 70% |
| Real Exam Qty: | 80 |
| Sample Questions: |  |
| Exam Way: | Online proctored exam or at authorized testing centers worldwide |
| Pre Condition: | Candidates should have a foundational understanding of ISO/IEC 27001 and audit principles. It is recommended (but not mandatory) to have completed the PECB ISO/IEC 27001 Lead Implementer training or equivalent experience. |
| Official Syllabus URL: | https://pecb.com/en/education/iso-iec-27001-lead-auditor |
PECB ISO-IEC-27001-Lead-Auditor日本語 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Audit Principles and Audit Process | 20% | - Audit types and stages ( initiation, planning, execution, reporting) - Risk-based audit approach - Audit evidence collection techniques - Audit sampling methodology - Audit scope and objectives |
| Topic 2: Information Security Management Systems (ISMS) and the ISO/IEC 27001 Standard | 15% | - Overview of ISO/IEC 27001 and its relationship with ISO/IEC 27002 - Fundamental principles and concepts of information security - Regulatory and legal considerations in information security |
| Topic 3: Certification and Accreditation Framework | 15% | - Certification decision process - Surveillance and re-certification audits - Principles of certification bodies - Audit report preparation and documentation - ISO/IEC 17021-1 requirements for certification bodies |
| Topic 4: Audit Lifecycle and Competencies of the Lead Auditor | 25% | - Conflict resolution during audits - Managing audit relationships with audited parties - Audit follow-up and corrective action verification - Audit communication strategies - Leading an audit team |
| Topic 5: ISMS Audit Based on ISO 19011 and ISO/IEC 17021-1 | 25% | - Auditing organizational structure and roles - Auditing control selection and implementation (Annex A) - Measuring, monitoring, and reporting ISMS performance - Auditing risk assessment and treatment processes - Auditing leadership commitment - Auditing the context of the organization - Continual improvement processes |
PECB ISO-IEC-27001-Lead-Auditor日本語 Exam: Answers That Actually Help
The ISO-IEC-27001-Lead-Auditor日本語 exam is PECB's official certification test — passing it earns the ISO 27001 credential at the Professional level. It demands genuine, working knowledge rather than theory alone, which is why candidates who prepare casually tend to stumble. It also feeds into related credentials such as PECB ISO/IEC 27001 Lead Implementer, PECB ISO/IEC 27001 Foundation, extending its value beyond one certificate.
Protection and delivery, both in writing. Delivery: the ISO-IEC-27001-Lead-Auditor日本語 product reaches your mailbox within one minute of payment; if nothing arrives within 2 hours, check spam and contact support for an immediate resend. Refund: sit the corresponding ISO-IEC-27001-Lead-Auditor日本語 exam within 60 days of purchase, and if you fail, apply with a scanned enrollment slip and the official Score Report PDF within 2 days after the exam — refunds complete within 7 days. The policy covers the corresponding exam only; attempts within 3 days of purchase, exams never actually taken, free materials, and expired orders are excluded, and the candidate name must match the payer name. Prefer to keep going? Exchange your product for two free exam products of equal value instead — the update service on your original purchase stays active.
The PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) exam costs USD 500 per attempt, with 70% as the passing mark. Fail, and USD 500 is payable again — the price of walking in half-prepared. A practical safeguard: practice with Prep4SureReview until your timed mock results clear 70% comfortably, then book the ISO-IEC-27001-Lead-Auditor日本語 exam.
Candidates should have a foundational understanding of ISO/IEC 27001 and audit principles. It is recommended (but not mandatory) to have completed the PECB ISO/IEC 27001 Lead Implementer training or equivalent experience. Eligibility requirements come from PECB and can be revised, so confirm the current rules on the official exam page: https://pecb.com/en/education/iso-iec-27001-lead-auditor before committing to a PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) registration.
The PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) exam is organized into 5 knowledge areas, with Audit Principles and Audit Process (20%), Information Security Management Systems (ISMS) and the ISO/IEC 27001 Standard (15%), Audit Lifecycle and Competencies of the Lead Auditor (25%) among the most significant. Allocate study time to match those weights, and see the outline section above for the complete list.
80 questions in 180 minutes — that is the PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) exam in numbers. The per-question budget is tight, and hesitation is what eats it. Train the pace deliberately: run full timed simulations in the Prep4SureReview engine, practice committing to an answer and moving on, and the real ISO-IEC-27001-Lead-Auditor日本語 exam will feel familiar instead of frantic.
You can — the Prep4SureReview free demo covers the PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) material, so download some sample questions and answers first and judge quality yourself. Once you buy, 365 days of free updates are included; after that period, extend the update service at a 50% discount from your member zone.
PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) Sample Questions:
金融会社であるPayBellは、会計ソフトウェアを使用して財務取引を追跡しています。このソフトウェアは、インターネット接続があればどこからでもアクセスできます。また、PayBellの従業員が互いに簡単に連携し、正確な財務報告を確実に行えるようにしています。PayBellはどのようなサービスを利用しているのでしょうか?
- A. 機械学習
- B. クラウドコンピューティング
- C. 人工知能
Correct Answer: B 🗳️
ビジネスプロセスの計画・実行・評価・改善サイクルにおける「計画」に当てはまるフレーズは次のうちどれか2つはどれですか?
* 文書の保管
- A. 目標設定
- B. 組織変更
- C. 文書の保管
- D. ICT資産の提供
- E. スタッフのトレーニング
Correct Answer: D,E 🗳️
Explanation: Only visible for Prep4SureReview members. You can sign-up / login (it's free).
あなたは監査チームリーダーとして、初めて第三者機関によるISMS監視監査を実施しています。現在、監査チームの別のメンバーと共に、被監査企業のデータセンターにいます。
同僚は情報セキュリティイベントと情報セキュリティインシデントの違いがよく分かっていないようです。あなたは例を挙げてその違いを説明しようと試みます。
以下のシナリオのうち、情報セキュリティインシデントと定義できるものはどれですか?(3つ)
- A. 組織が第三者による侵入テストに不合格となった。
- B. 従業員が勤務終了時に机を片付けなかった
- C. 未払いの請負業者がトップマネジメントのICTアカウントを削除する
- D. 組織のマルウェア対策ソフトウェアがウイルスを阻止します
- E. 不満を抱えた従業員が許可なく給与記録を変更する
- F. 組織のマーケティングデータがハッカーによってコピーされ、競合他社に売却される
- G. ハードディスクドライブが推奨交換時期を過ぎて使用されている場合
- H. 組織がフィッシングメールを受信しました
Correct Answer: C,E,F 🗳️
Explanation: Only visible for Prep4SureReview members. You can sign-up / login (it's free).
シナリオ3:NightCoreは、米国に拠点を置く多国籍テクノロジー企業で、電子商取引、クラウドコンピューティング、デジタルストリーミング、人工知能に重点を置いています。情報セキュリティマネジメントシステム(ISMS)を導入してから8か月以上経過した後、ISO/IEC 27001の認証を取得するために、認証機関に第三者監査の実施を依頼しました。
認証機関は7名の監査員からなるチームを編成した。その中で最も経験豊富なジャックが監査チームのリーダーに任命された。彼は長年にわたり、ISO/IEC 27001主任監査員、CISA、CISSP、CISMなど、数々の著名な資格を取得してきた。
ジャックは、NightCore が実装したすべての情報セキュリティ要件とコントロールを調査および評価することにより、ISMS 監査の各フェーズで徹底的な分析を実施しました。ステージ 2 監査中に、ジャックはいくつかの不適合を検出しました。ソフトウェア ライセンスの購入請求書の数をソフトウェア インベントリと比較した後、ジャックは、会社が多くのコンピュータでソフトウェアの違法バージョンを使用していることを発見しました。彼は、この不適合について経営陣に説明を求め、彼らがこれを認識しているかどうかを確認することにしました。彼の次のステップは、NightCore の IT 部門を監査することでした。経営陣は、NightCore のシステム管理者であるトムをガイド役として任命し、ジャックと監査チームがシステムの内部構造とデジタル資産インフラストラクチャを調査できるようにしました。
監査担当者は財務部の職員に聞き取り調査を行った際、同社が最近、コンサルタントの一人に対して異常に高額な取引を行っていたことを発見した。取引に関する必要な詳細情報をすべて収集した後、ジャックは経営陣に直接聞き取り調査を行うことにした。
最初の不適合について話し合った際、経営陣はジャックに対し、コピー版ソフトウェアの方が安価だったため、オリジナル版ではなくコピー版を使用することに意図的に決めたと説明した。ジャックはナイトコアの経営陣に対し、違法バージョンのソフトウェアを使用することはISO/IEC 27001の要件および国内法規に違反すると説明したが、彼らは特に問題視していないようだった。
監査から数か月後、ジャックは監査中に収集したナイトコアの情報の一部を、ナイトコアの競合他社に巨額の金銭で売却した。
このシナリオに基づいて、次の質問に答えてください。
シナリオ3に基づくと、NightCoreは不正なバージョンのソフトウェアを使用した際に、ISO/IEC 27001のどの管理項目を無視したのでしょうか?
- A. 附属書A 5.32 知的財産権
- B. 付属書A 5.10 情報およびその他の関連資産の許容される使用
- C. 付録A 5.1 情報セキュリティに関する方針
Correct Answer: A 🗳️
Explanation: Only visible for Prep4SureReview members. You can sign-up / login (it's free).
あなたは、医療サービスを提供する高齢者向け介護施設でISMS監査を実施しています。監査計画の次のステップは、情報セキュリティインシデント管理プロセスを検証することです。ITセキュリティマネージャーは、情報セキュリティインシデント管理手順を提示し、そのプロセスがISO/IEC 27035-1:2016に基づいていることを説明します。
文書を確認すると、「情報セキュリティ上の弱点、事象、およびインシデントは、特定後1時間以内に連絡担当者(PoC)に報告しなければならない」という記述が見つかりました。スタッフにインタビューしたところ、「弱点、事象、およびインシデント」の意味について、理解に違いがあることがわかりました。
過去6か月間のイベント追跡システムからインシデント報告記録をサンプリングし、その結果を以下の表にまとめました。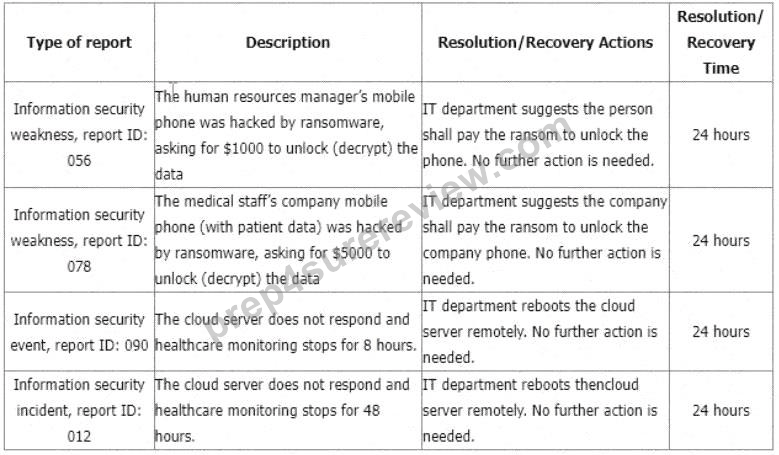
監査証拠をさらに収集するために、他の分野についても調査を進めたいと考えています。監査証跡に残らない項目を2つ選択してください。
- A. 会社が身代金を支払って会社の携帯電話とデータのロックを解除した方法と時期(クレジットカード、銀行振込など)について、より多くの証拠を収集する。(管理A.5.26に関連)
- B. 人事部長が個人のモバイルデータのロックを解除するために身代金を支払った方法と時期(クレジットカードや銀行振込など)について、より多くの証拠を収集する。(管理策A.5.26に関連)
- C. 組織がインシデント復旧時間をどのように決定したかについて、より多くの証拠を収集する。(管理策A.5.27に関連)
- D. 報告プロセスに対する理解について、より多くのスタッフにインタビューを行い、証拠をさらに収集する。
(管理項目A.6.8に関連) - E. 組織が事件後、それ以上の措置は不要と判断した経緯について、より多くの証拠を収集する。(管理策A.5.26に関連)
- F. インシデント復旧手順に関する証拠をさらに収集する。(管理策A.5.26に関連)
Correct Answer: A,B 🗳️
Explanation: Only visible for Prep4SureReview members. You can sign-up / login (it's free).
Viewing page 1 out of 84 pages.
Viewing questions 1-5 out of 418 questions.